Do you know what Behavioral Analytics in XDR is, and why organizations consider this thing while improving their security measures? If not, then you are in the right place. Here, we will talk about what behavioral analytics is and related benefits in detail.
Moreover, we will introduce you to a reliable XDR embedded security solution offered by a reputable VAPT service provider. What are we waiting for? Let’s explore more about it!
What Is Behavioral Analytics in XDR?
In order to provide dynamic operating baselines for users and entities, behavioral analytics in Extended Detection and Response (XDR) continuously ingests and correlates cross-layered telemetry across endpoints, networks, identities, cloud workloads, and email gateways.
It automatically identifies abnormal patterns, evasive lateral movement, and insider threats that get beyond static, rule-based signature protections by comparing real-time activity to these baselines.
By correlating low-fidelity signals across many attack surfaces, this automated risk-scoring process enables Security Operations Center (SOC) teams to identify high-confidence compromises and significantly shorten Mean Time to Detect (MTTD).
Let’s take a look at what Behavioral Analytics in XDR is, its uses, its features, and related benefits for users!
Why Does Behavioral Analytics in XDR Matter?
Behavioral analytics in XDR matters for the following reasons:
1. Detects Unknown & Zero-Day Threats: Instead of using established file signatures, it uses anomalous operational execution pathways to detect malicious activities.
2. Correlates Cross-Domain Multi-Vector Attacks: Creates a single incident timeline by connecting separate anomalous signals from endpoint, identity, cloud, network, and email telemetry.
3. Exposes Compromised Credentials & Insider Threats: Identifies lateral movement, unusual user behavior, and the exploitation of stolen, valid access keys to escalate privileges.
4. Drastically Reduces Alert Fatigue: Aggregates low-fidelity alerts into high-confidence, targeted behavioral occurrences to filter out noise.
5. Accelerates Mean Time to Detect (MTTD) & Respond (MTTR): Initial threat validation is automated, and machine-speed cross-layered reaction operations are coordinated.
Behavioral Analytics vs. Traditional Rule-Based Detection
|
S.No. |
Topics |
Factors |
What? |
|
1. |
Behavioral Analytics |
Dynamic Baseline Intelligence |
Identifies undiscovered anomalies and zero-day execution paths without depending on existing signs by establishing typical activity patterns across user identities, endpoints, and networks. |
|
Cross-Layered Contextual Correlation |
Creates cohesive, high-confidence incident stories by ingesting and connecting low-fidelity telemetry from several vectors (email, cloud, identity, endpoint). |
||
|
2. |
Traditional Rule-Based Detection |
Static Signature Reliance |
Fails to identify new or altered threats by evaluating telemetry rigorously against static "if-then" rules and stringent, predetermined indicators of compromise (IOCs). |
|
High Operational Noise & Alert Fatigue |
Disconnected triggers, isolated event alerts, and an excessive amount of false positives and uncontextualized noise overwhelm SOC analysts. |
Key Components of Behavioral Analytics in XDR
The following are some key components of behavioral analytics in XDR:
● User & Entity Behavior Analytics (UEBA): To identify unusual behavior, baseline the typical activity patterns of individuals, devices, and service accounts.
● Cross-Vector Telemetry Correlation Engine: Unifies incident stories by ingesting and stitching telemetry across networks, email, identities, endpoints, and the cloud.
● Machine Learning & Statistical Anomaly Models: Uses both trained and unsupervised models to find undiscovered zero-day execution routes and minute deviations.
● Dynamic Risk Scoring Framework: Gives entities varying, real-time risk rankings based on asset criticality and cumulative threat intensity.
● Automated SOAR & Orchestration Integration: When dynamic risk thresholds are exceeded, automated containment workflows across security products are triggered.
How Does Behavioral Analytics Work in XDR?
Behavioral analytics works in XDR in the following ways:
a) Continuous Telemetry Ingestion: Gathers detailed log and event data in real time from email gateways, cloud workloads, endpoints, identities, and network traffic.
b) Baseline Profiling: Establishes typical operational behavioral baselines for each person, device, and application within the company using machine learning models.
c) Anomaly Detection & Correlation: Cross-correlates multi-vector warnings into cohesive, context-rich threat timelines and detects departures from predetermined baselines.
d) Dynamic Risk Scoring: Uses attack intensity and asset business value to determine real-time threat scores for compromised assets and identity accounts.
e) Automated Response Triggering: When risk scores exceed predetermined criteria, specified response playbooks are carried out, such as isolating hosts, canceling sessions, or quarantining communications.
Role of AI and Machine Learning in XDR Behavioral Analytics
|
S.No. |
Factors |
What? |
|
1. |
Automates Dynamic Baseline Creation |
Without the need for manual threshold configuration, it continuously maps complicated, typical user and system operating patterns. |
|
2. |
Detects Evasive & Stealthy Anomalies |
Uses unsupervised learning models to identify living-off-the-land strategies and subtle, zero-day threat behaviors. |
|
3. |
Executes Cross-Vector Threat Correlation |
Connects low-fidelity signals across endpoint, network, identity, and email vectors into cohesive incident stories. |
|
4. |
Powers Adaptive Risk Scoring |
Evaluates event severity, past performance, and asset criticality to recalculate entity risk scores in real time. |
|
5. |
Drives Autonomous Response Orchestration |
Initiates automated, high-confidence containment playbooks at machine speed to reduce risks before harm is done. |
Common Threats Identified Through Behavioral Analytics
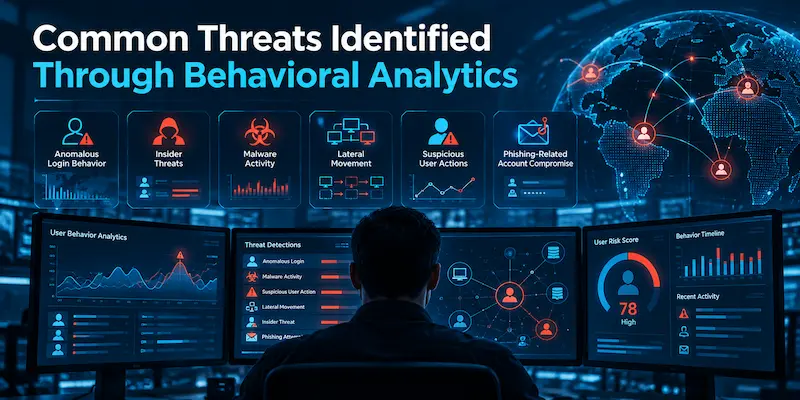
The following are some common threats identified through behavioral analytics:
1. Credential Compromise & Account Takeover (ATO): Detects concurrent sessions circumventing MFA protections, unusual login locations, and impossible travel.
2. Insider Threats & Data Exfiltration: Identifies unusual outbound traffic patterns, large data downloads, and illegal access to private files.
3. Living-off-the-Land (LotL) Attacks: Detects malevolent misuse of authorized administrative tools such as PsExec, PowerShell, or WMI.
4. Evasive Ransomware Execution: Detects unwanted process injection, shadow copy deletions, and quick host encryption attempts.
5. Lateral Movement & Privilege Escalation: Monitors attempts at unauthorized administrative access, kerberoasting, and strange service account behavior.
How Does Behavioral Analytics Help Reduce False Positives?
Behavioral analytics help reduce false positives in the following ways:
● Filters Noise via Contextual Baselining: To differentiate between normal operational changes and real threat behaviors, anomalies are compared to previous operational baselines.
● Correlates Multi-Vector Telemetry: Suppresses low-fidelity, isolated warnings via email, networks, and endpoints unless cross-domain signs are present.
● Eliminates Rigid Static Thresholds: Substitutes dynamic, machine learning-driven anomaly detection for general, rule-based triggers that activate on innocuous activities.
● Weights Risk by Entity Criticality: Filters out low-impact deviations and ranks warnings according to asset sensitivity and user access levels.
● Aggregates Signals into Unified Incidents: Instead of producing hundreds of unnecessary alerts, it combines several connected suspicious occurrences into a single actionable incident.
Challenges and Limitations of Behavioral Analytics in XDR
|
S.No. |
Factors |
What? |
|
1. |
Initial Training & Baseline Period |
Before correctly differentiating between legitimate threats and routine behavior, weeks of clear historical data are needed. |
|
2. |
Telemetry Gaps & Ingestion Quality |
The accuracy of the correlation engine is directly impacted by missing log sources or inadequate data standardization. |
|
3. |
Evolving & Legitimate Operational Changes |
False-positive increases could be caused by abrupt changes in user roles, software updates, or workflows. |
|
4. |
Slow-and-Stealthy Adversary Evasion |
It is possible for sophisticated attackers to blend into updated baseline standards over long periods of time. |
|
5. |
High Data Storage & Compute Costs |
Large amounts of cloud resources are required to process and store enormous cross-vector behavioral telemetry streams. |
Best Practices for Implementing Behavioral Analytics in XDR
The following are the best practices for implementing behavioral analytics in XDR:
a) Ensure Full Cross-Domain Telemetry Coverage: To remove blind spots, integrate telemetry across endpoint, network, identity, cloud, and email vectors.
b) Establish Adequate Baseline Observation Windows: Before imposing auto-containment, give machine learning models enough time to understand actual operational rules.
c) Normalize and Standardize Ingested Data: To guarantee smooth cross-vector correlation, schema-map all multi-vendor log sources to shared data models.
d) Align Dynamic Risk Scoring with Business Criticality: Modify entity risk weights to account for executive positions, sensitive data locations, and crown jewel assets.
e) Implement Tiered Automated Response Playbooks: Before moving on to complete automated host isolation or account suspension, start with low-friction automated alerts.
Future of Behavioral Analytics in XDR
Predictive, agentic AI systems that move SecOps from reactive anomaly detection to autonomous threat avoidance are the key to the future of behavioral analytics in XDR. In addition to keeping an eye on conventional endpoints, these models will continuously assess intent across identity layers, AI agents, and non-human workloads, carrying out context-aware remediation at machine speed before zero-day assaults can manifest.
Conclusion
Now that we have talked about what Behavioral Analytics in XDR is, you might want to get your hands on a dedicated security solution against future threats. For that, you can go for ShieldXDR, a dedicated threat detection and response tool offered by Craw Security.
ShieldXDR can help users with a robust cybersecurity solution, because it acts as it automatically detects any unusual cyber threats and vulnerabilities. Thus, you can rely on this amazing tool. What are you waiting for? Contact, Now!
Frequently Asked Questions
About Behavioral Analytics in XDR
1. What Is Behavioral Analytics in XDR?
Behavioral Analytics in Extended Detection and Response (XDR) is an integrated capability that automatically identifies aberrant, multi-vector cyber threats in real time by continuously analyzing cross-domain telemetry to baseline normal entity behavior.
2. How Does Behavioral Analytics Work in XDR?
Behavioral analytics works in XDR in the following ways:
a) Cross-Vector Data Ingestion,
b) Continuous Behavioral Baselining,
c) Multi-Domain Anomaly Correlation,
d) Real-Time Dynamic Risk Scoring, and
e) Autonomous Response Orchestration.
3. Why Is Behavioral Analytics Important for XDR?
Behavioral analytics is important for XDR for the following reasons:
a) Bypasses Signature Limitations,
b) Correlates Multi-Vector Attacks,
c) Exposes Insider Threats & Stolen Credentials,
d) Drastically Reduces Alert Fatigue, and
e) Drives Down MTTD and MTTR.
4. How Does XDR Use AI and Machine Learning for Behavioral Analysis?
XDR uses AI and ML for behavioral analytics in the following ways:
a) Automates Dynamic Baselining,
b) Detects Evasive & Unknown Threats,
c) Executes Cross-Domain Event Correlation,
d) Calculates Adaptive Risk Scores, and
e) Drives Autonomous Remediation Playbooks.
5. What Types of Threats Can Behavioral Analytics Detect?
Behavioral analytics can detect the following types of threats:
a) Account Takeover & Credential Abuse,
b) Insider Threats & Data Exfiltration,
c) Living-off-the-Land (LotL) Exploitation,
d) Evasive Ransomware Execution, and
e) Lateral Movement & Privilege Escalation.
6. How Does Behavioral Analytics Reduce False Positives in XDR?
Behavioral analytics reduces false positives in XDR in the following ways:
a) Contextual Baseline Verification,
b) Multi-Vector Signal Correlation,
c) Dynamic Adaptive Thresholds,
d) Entity Criticality Weighting, and
e) Alert Aggregation into Incidents.
7. What Is the Difference Between Behavioral Analytics and Rule-Based Detection?
While rule-based detection tightly compares incoming telemetry against static, predetermined signatures and "if-then" logic, behavioral analytics continuously assesses entity activity against machine-learned dynamic baselines to identify unexpected threats.
8. How Does Behavioral Analytics Help Detect Insider Threats?
Behavioral analytics helps detect insider threats in the following ways:
a) Baselines Normal Work Patterns,
b) Flags Unusual Data Access & Aggregation,
c) Monitors Exfiltration Channels,
d) Detects Privilege Escalation & Abuse, and
e) Incorporates HR & Behavioral Context.
9. What Are the Challenges of Using Behavioral Analytics in XDR?
The following are the challenges of using behavioral analytics in XDR:
a) Warm-Up Baseline Overhead,
b) Telemetry Quality Dependence,
c) Operational Shift Disruption,
d) Low-and-Slow Attack Evasion, and
e) High Infrastructure Costs.
10. How Can Organizations Implement Behavioral Analytics in an XDR Platform?
Organizations can implement behavioral analytics in an XDR platform in the following ways:
a) Integrate Comprehensive Telemetry Sources,
b) Establish an Adequate Baseline Window,
c) Standardize and Schema-Map Ingested Data,
d) Configure Dynamic, Context-Aware Risk Rules, and
e) Deploy Tiered Response Playbooks.