Do you know what Machine Learning and XDR are and how organizations use them to improve security measures for future threats? If not, then you are in the right place. Here, we will talk about what ML and XDR are and related benefits in detail.
Moreover, we will introduce you to a reliable security solution offered by a reputable VAPT service provider. What are we waiting for? Let’s get started!
What Is XDR Threat Detection?
A security architecture called Extended Detection and Response (XDR) automatically gathers, correlates, and analyzes data from a variety of sources on a single, unified platform, including endpoints, network traffic, cloud workloads, email, and identity systems.
XDR replaces isolated security silos with centralized, high-confidence detection by combining these various data sources to offer comprehensive visibility into intricate threat chains. Threat hunters and security operations center (SOC) teams may identify complex threats more quickly and carry out automated, multi-layered containment activities from a single control plane thanks to this cross-domain context.
Let’s explore Machine Learning and XDR, their uses, their capabilities, and related benefits for organizations in the IT Industry!
Why Is Machine Learning Essential for Modern XDR?
|
S.No. |
Factors |
Why? |
|
1. |
Automates Multi-Domain Data Correlation |
Quickly creates cohesive incident stories by connecting disparate data from endpoint, network, identity, and cloud telemetry. |
|
2. |
Detects Unknown Zero-Day and Anomaly Patterns |
Detects subtle behavioral abnormalities and hidden dangers without depending on static markers that already exist. |
|
3. |
Reduces Alert Fatigue via Dynamic Prioritization |
Only high-confidence, high-severity dangers are highlighted by filtering low-fidelity noise and grouping similar alarms. |
|
4. |
Accelerates Automated Incident Response |
As soon as complicated attack patterns are identified, cross-layered containment playbooks are immediately triggered. |
|
5. |
Adapts to Evolving Attacker Behaviors |
Keeps up with changing enemy strategies by continuously learning from baseline network and user activity. |
What Role Does Machine Learning Play in XDR?
ML plays the following role in XDR:
1. Automates Cross-Domain Data Correlation: Quickly combines telemetry from cloud, network, and endpoint layers to create cohesive attack narratives.
2. Detects Zero-Day and Anomaly Patterns: Highlights subtle behavioral abnormalities and hidden risks without depending on static signature matching.
3. Drives Dynamic Alert Prioritization: Suppresses noise and reveals high-confidence security incidents by correlating heterogeneous low-fidelity events.
4. Accelerates Automated Incident Containment: As soon as malicious behaviors are detected, it immediately orchestrates multi-layered response playbooks.
5. Continuously Adapts to Evolving TTPs: Dynamically modifies baseline models to identify new attack infrastructure and evolving opponent tactics.
Machine Learning Techniques Used in XDR
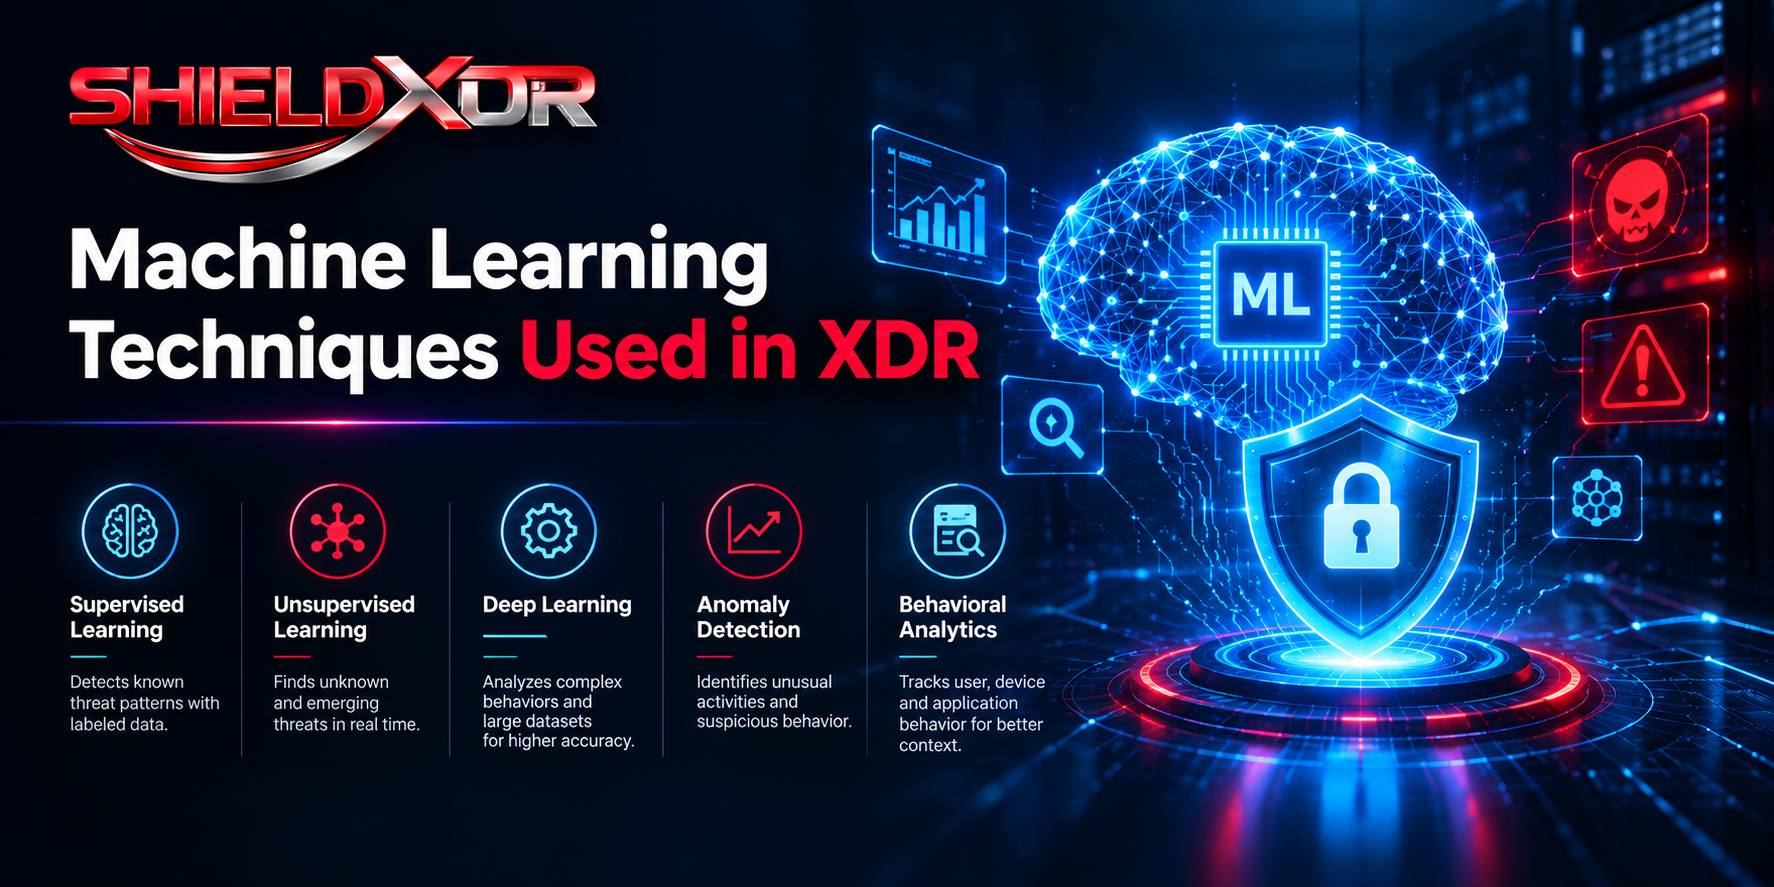
ML techniques are used in XDR:
● Behavioral Baselining and Anomaly Detection: Uses unsupervised machine learning to identify minor deviations and continually simulate typical entity activity.
● Predictive Threat Scoring and Correlation: Evaluates multi-vector telemetry, computes real-time risk scores, and maps attacks using supervised models.
How Does Machine Learning Help XDR Detect Modern Cyberattacks?
|
S.No. |
Factors |
How? |
|
1. |
Establishes Dynamic Behavioral Baselines |
Monitors typical network, host, and user activities to quickly identify minute operational irregularities. |
|
2. |
Correlates Cross-Domain Telemetry |
Unifies disparate telemetry from identity, endpoint, network, and cloud vectors into a single incident. |
|
3. |
Detects Zero-Day and Living-off-the-Land Tactics |
Detects new exploits and questionable native tool usage without depending on known signatures. |
|
4. |
Suppresses Noise and Prioritizes Threats |
High-confidence, actionable occurrences are revealed by filtering low-fidelity alerts and grouping similar events. |
|
5. |
Triggers Automated Multi-Layered Containment |
Carries out quick cross-stack response activities as soon as malicious activity is verified. |
How Does Machine Learning Improve XDR Threat Detection?
ML improves XDR threat detection in the following ways:
a) Detects Unknown and Emerging Threats: Identifies signatureless attack techniques and zero-day exploits by examining unusual behavioral variations among systems.
b) Reduces False Positives: Isolates genuine, high-confidence security occurrences by contextualizing cross-domain data and removing common network noise.
c) Accelerates Threat Detection and Response: Automatically carries out quick, multi-layered containment steps by processing enormous amounts of telemetry in real time.
Benefits of Using Machine Learning in XDR
The following are the benefits of using ML in XDR:
1. Proactive Zero-Day & Anomaly Detection: Finds behavioral abnormalities and hidden exploits before updates are released by conventional signature databases.
2. Intelligent Noise Suppression: Reduces alert fatigue for security analysts significantly by grouping related occurrences and filtering out normal, non-malicious anomalies.
3. Automated Cross-Domain Correlation: Creates a cohesive, actionable attack story by connecting discrete telemetry from endpoint, network, identity, and cloud vectors.
4. Accelerated Mean Time to Detect and Respond (MTTD/ MTTR): Rapidly analyzes large data streams and initiates automatic playbooks to thwart threats in real time.
5. Adaptive Security Baselines: Automatically modifies detection thresholds without the need for human calibration by continuously learning changing environmental standards.
Best Practices for Implementing Machine Learning in XDR
|
S.No. |
Factors |
What? |
|
1. |
Ensure High-Quality, Standardized Telemetry |
Logs from all vector integrations should be cleaned and normalized before being incorporated into ML training processes. |
|
2. |
Establish Robust Environmental Baselines |
To accurately represent typical network behavior, give models enough time to observe under benign conditions. |
|
3. |
Combine ML Detection with Rule-Based Controls |
For balanced detection coverage, combine probabilistic machine learning models with deterministic signature criteria. |
|
4. |
Implement Continuous Model Tuning and Validation |
To avoid bias and drift, retrain and evaluate models on a regular basis using new threat data. |
|
5. |
Maintain Human-in-the-Loop Oversight |
To prevent unintentional disruption, analyst authentication is needed for high-impact automated response activities. |
The Future of Machine Learning and XDR Threat Detection
Deep behavioral learning and generative AI agents are driving the future of machine learning in XDR toward autonomous, predictive defense. Next-generation XDR platforms will automatically build self-healing zero-trust perimeters, conduct cross-domain containment in milliseconds with little human intervention, and dynamically model threat actor behaviors rather than just identifying current anomalies.
Conclusion
Now that we have talked about what Machine Learning and XDR are, you might want to get your hands on a dedicated XDR solution from a reliable source. For that, you can go for ShieldXDR, a dedicated threat detection and response tool offered by Craw Security.
ShieldXDR can help businesses by finding unknown vulnerabilities in networks and systems while responding to cyberattacks to ensure data security. What are you waiting for? Contact, Now!
Frequently Asked Questions
About Machine Learning and XDR
1. How does machine learning improve XDR threat detection?
ML improves XDR threat detection in the following ways:
a) Automates Cross-Domain Telemetry Correlation,
b) Uncovers Zero-Day and Signatureless Threats,
c) Suppresses Noise to Reduce Alert Fatigue,
d) Establishes Dynamic Behavioral Baselines, and
e) Triggers Automated Cross-Stack Containment.
2. Can machine learning detect unknown cyber threats?
Yes, machine learning does not rely on pre-existing signs to detect unknown cyber threats; instead, it does so by identifying aberrant behavioral patterns and departures from established system baselines.
3. Does ML-powered XDR reduce false positives?
Yes, by linking isolated abnormalities across many telemetry domains, eliminating routine background noise, and verifying suspicious activity against dynamic environmental baselines, ML-powered XDR lowers false positives.
4. What types of attacks can machine learning detect?
ML can detect the following types of attacks:
a) Zero-Day and Unseen Malware,
b) Insider Threats and Credential Compromise,
c) Living-off-the-Land (LotL) Attacks,
d) Data Exfiltration and Lateral Movement, and
e) Automated Botnet and Brute-Force Operations.
5. What is the difference between AI and machine learning in XDR?
In XDR, machine learning is the particular algorithmic toolset within artificial intelligence that analyzes raw data and identifies attack patterns, while artificial intelligence acts as the general intelligence layer that automates reasoning, context generation, and judgments throughout the system.
6. Is machine learning enough for effective XDR security?
No, machine learning by itself is insufficient for effective XDR; a hybrid strategy that incorporates deterministic, rule-based controls, high-quality threat intelligence, human-in-the-loop analyst monitoring, and ML-driven behavioral analytics is needed.
7. How can AI improve threat detection and response?
AI can improve threat detection and response in the following ways:
a) Automates Natural Language Investigation,
b) Executes Autonomous Incident Triage,
c) Generates Dynamic Response Playbooks,
d) Predicts Threat Propagation, and
e) Accelerates Threat Intelligence Synthesis.
8. How does AI benefit an advanced persistent threat?
AI benefits an advanced persistent threat in the following ways:
a) Automates Spear-Phishing and Reconnaissance,
b) Generates Polymorphic Malware,
c) Accelerates Automated Vulnerability Discovery,
d) Optimizes Living-off-the-Land (LotL) Tactics, and
e) Evasion of Behavioral ML Baselines.
9. How can AI be used for intrusion detection?
AI can be used for intrusion detection in the following ways:
a) Real-Time Network Anomaly Profiling,
b) Host and Log Behavior Analytics,
c) Automated Encrypted Traffic Analysis,
d) Predictive Signatureless Threat Identification, and
e) Self-Tuning Alert Filtering.
10. Can machine learning be used to detect phishing attacks?
Yes, machine learning uses real-time analysis of email headers, domain age, structural layout, natural language purpose, and embedded URLs to identify phishing attacks and flag dangerous content independent of conventional blacklists.